
My Journey to Nokia Hall of Fame in Just 20min
bug bounty POC
Introduction
Hi, this is X84 , and I hope all of you are doing well. As a cybersecurity enthusiast, I am always on the lookout for opportunities to find vulnerabilities and report them to companies. Recently, I came across a medium post where someone mentioned making it to the Nokia Hall of Fame, and I was determined to make it there too. In just 20 minutes, I was able to find vulnerabilities that earned me a spot-on Nokia’s Honorary Hall of Fame list. In this article, I will share my journey and the steps I took to achieve this milestone.
Recon
My first step was to enumerate all the subdomains using subfinder .With Nokia being a huge target, all subdomains were in scope. Once I had my list of unique domains, I ran katana crawler to find all the URLS in this domains .....
// enumerate subdomains
subfinder -d nokia.com -o domains.txt
// Katana
katana -list domains.txt -o urls.txt
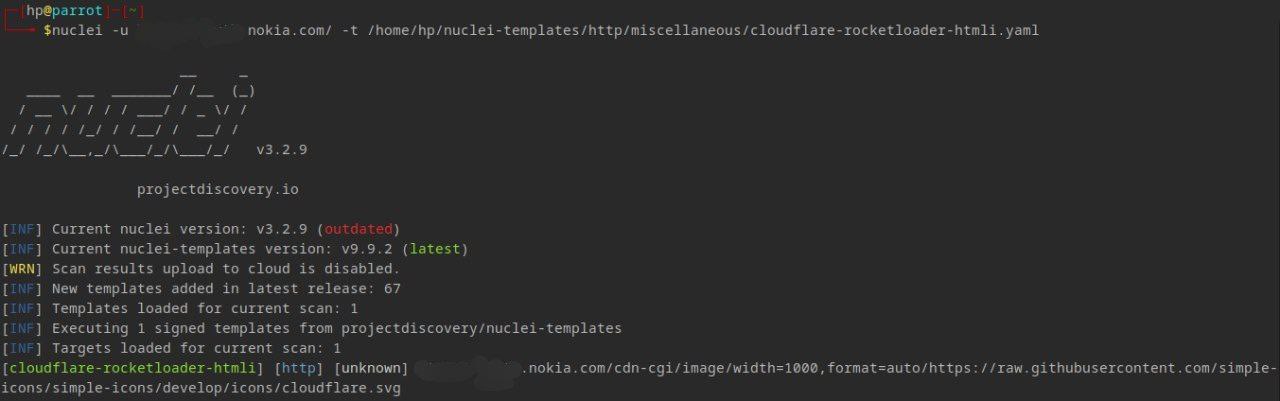
After taking a short break, I reviewed the results to find that I had found some URLS that contain "cdn-cgi" . I tried to run "cloudflare-rocketloader-htmli" nuclei template on this URLS and booom it worked successfully :
Response from Nokia
Dear Reporter,
Thank you very much for sending your findings to us.
We will list your findings to be fixed and add you to our Hall of fame.
How would you like your name to appear in the Hall of Fame?
We will use: ******* ******, if we don’t hear back from you.
Thank you again
Nokia Security Team
From: X84 < [email protected] >
Sent: Monday, June 24, 2024 11:14 PM
To: Security-Alert, ( Nokia - Global ) < [email protected] >
Subject: Cloudflare Rocket Loader HTML Injection Vulnerability
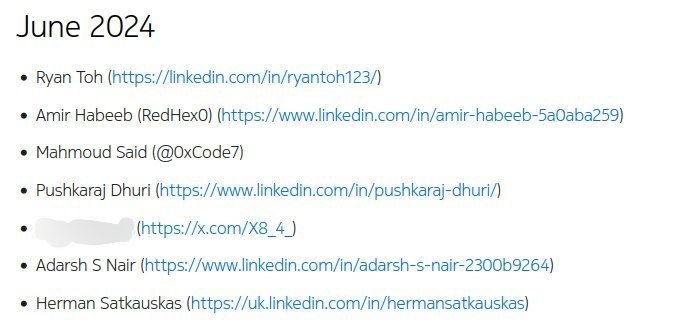
- After this , They added my name in their Hall Of Fame list :
Summary:
Cloudflare's Rocket Loader optimizes the delivery of JavaScript to improve page load times. However, its implementation in Nokia's authentication service allows manipulation of image URLs to load external content. An attacker can replace the image URL with any arbitrary URL, causing the affected page to load and display content from the specified URL.
Steps to Reproduce:
1- Navigate to the Original URL:
Open the following URL to see an example of the image served by Rocket Loader:
https://example.nokia.com/cdn-cgi/image/width=1000,format=auto/https://raw.githubusercontent.com/simple-icons/simple-icons/develop/icons/cloudflare.svg
2- Change the URL to point to a different image, such as:
https://example.nokia.com/cdn-cgi/image/width=1000,format=auto/https://initiate.alphacoders.com/download/images5/430064/png
3- You can replace the image URL with any valid URL to observe how different content is rendered on the affected page.
POC :
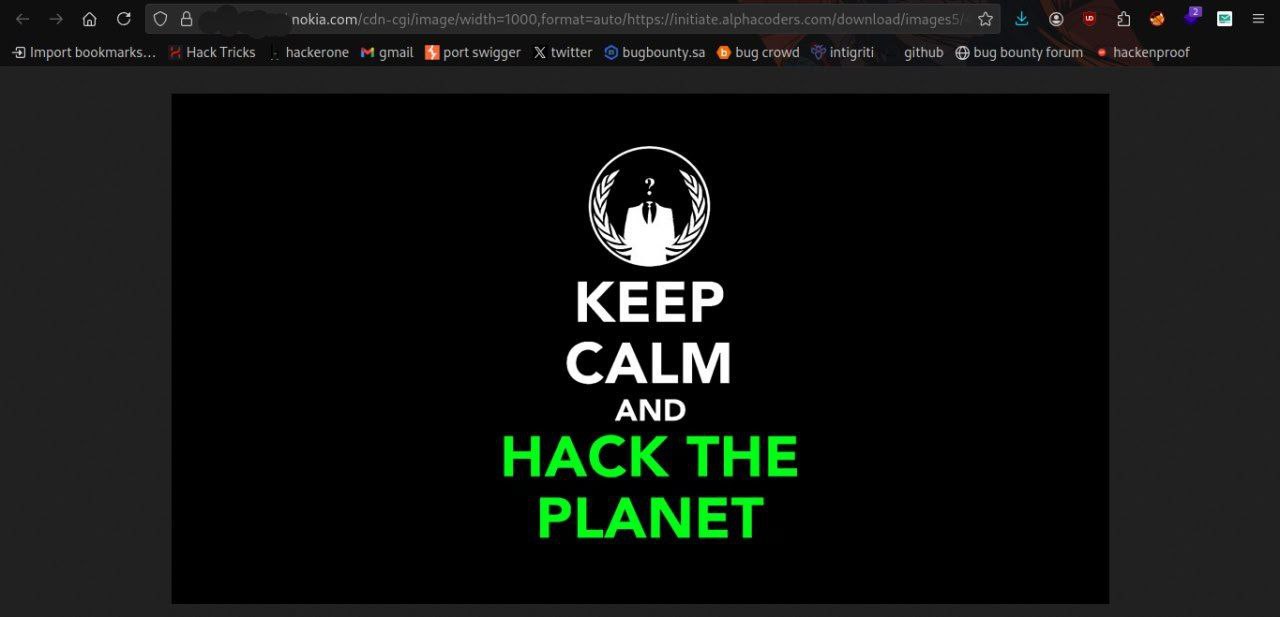
Impact:
- Content Spoofing: Attackers can replace legitimate images with misleading or malicious content. This could mislead users or provide false information, potentially damaging trust in the brand.
- Phishing: By injecting images that contain phishing content, attackers can trick users into revealing sensitive information. For instance, an image could be crafted to resemble a fake login form, capturing user credentials.
- Brand Damage: Displaying inappropriate or malicious images can tarnish Nokia’s reputation. Such images can damage the brand's public image, leading to decreased trust and credibility.
How to find it automatically using subfinder , katana , nuclei :
// enumerate subdomains :
subfinder -list domains.txt -o subdomains.txt
// Find URLS of Subdomains :
katana -list subdomains.txt -o ulrs.txt
// grep urls with " cdn-cgi " :
cat urls.txt | grep "cdn-cgi" >> target-ulrs.txt
// find the vulnerability using nuclei :
nuclei -list target-urls.txt -t / home / kali / nuclei-templates / http / miscellaneous/ cloudflare-rocketloader-htmli.yaml -o result.txt
Final thought
Reconnaissance is key! While using scanners can be helpful, luck often plays a role in finding valid vulnerabilities. It’s essential to conduct thorough reconnaissance to identify potential attack surfaces and vulnerabilities. By doing so, you increase your chances of finding vulnerabilities that scanners may not detect.
Thanks for reading!!! Happy Hacking!!!!
follow me on X — https://x.com/X8_4_
About the Creator
X84
too stupid to come up with a bio
Enjoyed the story? Support the Creator.
Subscribe for free to receive all their stories in your feed.
Comments
There are no comments for this story
Be the first to respond and start the conversation.