
Operationalizing AI Risk in Banking: 230 Controls, Three Frameworks, One Converging Deadline
The Treasury's FS AI RMF arrived in February. High-risk AI enforcement begins August 2. The governance debt banks accumulated for a decade is now due.
Fifty-one days separate today from August 2, 2026.
On that date, requirements for high-risk AI systems under Annex III of the EU AI Act become enforceable. The Act classifies systems that evaluate creditworthiness or establish credit scores, and systems used for risk assessment and pricing in life and health insurance, as high-risk by default. Fines reach EUR 35 million or 7% of global turnover.
That deadline lands on a calendar already crowded with obligations. DORA entered full enforcement on January 17, 2025, and applies to banks, insurers, investment firms, payment providers, and their third-party ICT service providers.
Then came the third piece. On February 19, 2026, the U.S. Department of the Treasury released two financial-sector AI resources: the Artificial Intelligence Lexicon and the Financial Services AI Risk Management Framework. The materials are non-binding, yet they are likely to become a reference in examinations, internal audit expectations, third-party oversight, and contract negotiations.
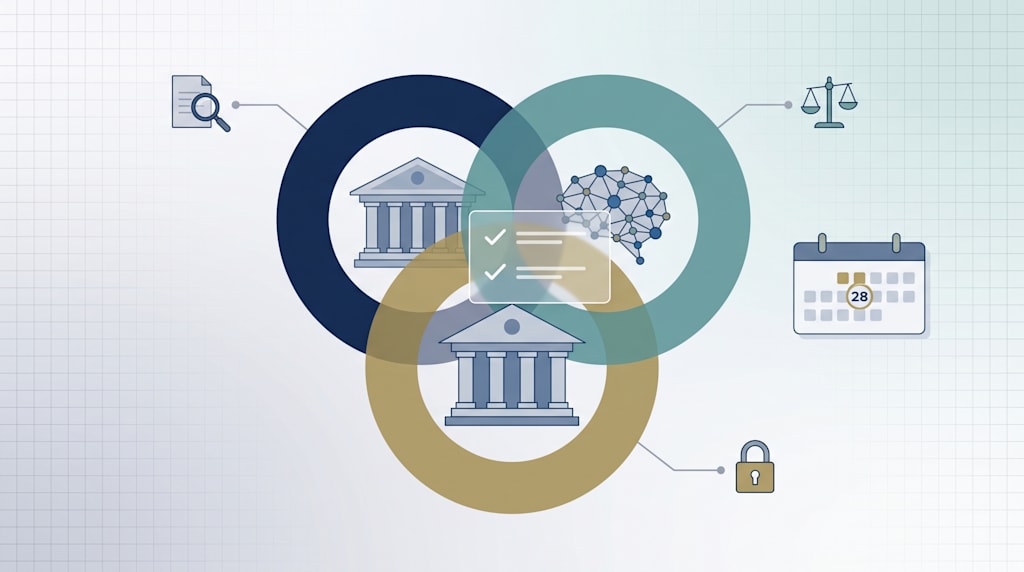
Three frameworks. Three jurisdictions of origin. One shared demand: prove you govern the AI you run.
The Debt Behind the Deadline
Banks did not arrive here unprepared by accident. They arrived here carrying debt.
Risk practitioners describe accumulated governance debt inside financial institutions: information sprawl, identity fragmentation, opaque model lifecycles, and infrastructure never designed for AI velocity.
Each item has a concrete shape. An opaque model lifecycle means nobody can name every model in production, who approved it, or what data trained it. Identity fragmentation means service accounts, API keys, and human credentials access models without a unified permission map. Infrastructure built for quarterly releases now hosts models that retrain weekly.
None of this blocked AI adoption. All of it blocks AI governance. Regulators now ask for evidence that the debt prevents banks from producing.
What the FS AI RMF Actually Contains
The Treasury framework gives the sector a shared answer sheet. Developed in coordination with more than 100 financial institutions, the Financial Services Sector Coordinating Council, and the Cyber Risk Institute, it introduces 230 control objectives across governance, data, model development, validation, monitoring, third-party risk, and consumer protection. Many controls map to specific system behaviors, ownership assignments, and evidence artifacts expected to withstand audit and supervisory review.
The framework adapts the NIST AI Risk Management Framework for financial institutions and is currently voluntary guidance, though it is expected to shape auditor standards as adoption accelerates.
The full text of the parallel European regulation sits in the official EU AI Act, Regulation (EU) 2024/1689. Reading the two side by side reveals heavy overlap. Inventory your systems. Govern your data. Validate before deployment. Monitor after. Document everything.
Where Model Risk Management Meets Security
Banks already run model risk management. The Federal Reserve's SR 11-7 guidance has shaped validation, inventory, and challenge processes since 2011. High-risk classification under the EU Act adds conformity assessment, technical documentation, structured data governance, logged human oversight, and post-market monitoring on top of SR 11-7 and ECB guide-to-internal-models expectations that most banks already run. SysArt Consulting
The new layer that catches teams off guard is security. AI systems carry an attack surface that traditional models never had. Prompt injection against LLM-based assistants. Data poisoning against training pipelines. Model extraction through repeated queries. Adversarial inputs that flip a fraud score.
AI security and risk management as a discipline merges two offices that historically worked apart. The model risk team validates accuracy and conceptual soundness. The security team defends the infrastructure. Neither alone covers a poisoned training set that produces a biased but technically functional credit model.
Secure AI deployment now has engineering specifics written into law. Article 10 requires a bias assessment of training data, affecting methodology. Article 14 requires interpretable outputs that support human oversight, affecting architecture choices. Article 12 requires automatic logging of inputs and outputs, requiring infrastructure changes to credit origination systems. These are engineering requirements, not documentation tasks.
Explainability as Audit Evidence
The examination question has changed. Supervisors no longer ask whether a model performs. They ask why it produced a specific decision for a specific customer.
Explainable AI banking systems answer that question at the individual decision level. Feature attribution shows which inputs drove a denial. Decision logs tie the attribution to a timestamp, a model version, and a human reviewer. The evidence package survives an audit two years later.
This expectation crosses borders. Singapore's monetary authority published its FEAT principles for fairness, ethics, accountability, and transparency years before the current wave. Supervisors across major banking markets now converge on the same core demand. A score without a reason no longer passes review.
The Operating Model That Makes It Work
Operationalizing an AI risk framework means assigning the 230 objectives to named owners.
Chief Risk Officers own the risk appetite statement and the tiering logic that decides which models get heavy scrutiny. Heads of AI governance own the living model inventory, the lifecycle gates, and the documentation standards. CISOs own identity controls, pipeline security, and adversarial testing.
The inventory deserves special attention. A spreadsheet updated annually fails the moment a team fine-tunes a model on Tuesday. The inventory has to be updated through the deployment pipeline itself. Registration becomes a release gate, never a follow-up task.
Most institutions lack the internal bandwidth to retrofit this across hundreds of models before the deadlines bite. Firms working in this space pair AI model governance design with the security engineering underneath it. Companies like ViitorCloud, which writes about AI security and risk management in banking, focus on the operational layer: inventory automation, control mapping, and audit-ready evidence trails that align to the published frameworks.
Fifty-one days is short. The frameworks are public. The control objectives are numbered. The institutions that assign owners now will spend 2027 refining a working system. The institutions that wait will spend it explaining gaps to examiners.
----------------------------------------------------------------------------------------
Frequently Asked Questions
How do banks govern AI risk?
Banks maintain a model inventory, tier systems by risk, validate before deployment, log decisions, and assign named control owners.
What is the FS AI RMF?
A voluntary U.S. Treasury framework from February 2026 offering 230 control objectives for governing AI across financial institutions.
Which banking AI systems count as high-risk under the EU AI Act?
Credit scoring, creditworthiness evaluation, and life or health insurance risk pricing systems qualify as high-risk by default.
What is explainable AI in banking?
Systems that show which factors drove each decision, with logged evidence that regulators and auditors can review later.
About the Creator
ViitorCloud Technologies
As a leading software development company, we’ve empowered 500+ startups, SMBs, and enterprises to transform their operations. Upgrade your business with our AI-First Software and Platforms that automate and scale, keeping you future-ready.
Enjoyed the story? Support the Creator.
Subscribe for free to receive all their stories in your feed.
Comments
There are no comments for this story
Be the first to respond and start the conversation.