
Eos Investment Alliance on How Blockchain Architecture Is Evolving
Research into modular systems, interoperability protocols, and the engineering behind next generation networks
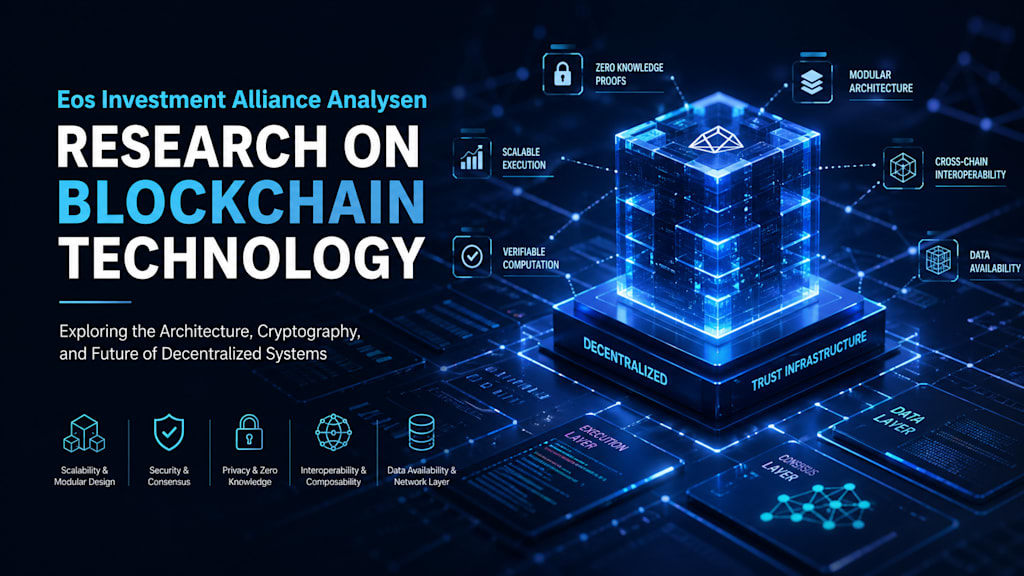
Blockchain architecture has evolved from a narrowly defined transaction ledger into a multi-layered computational infrastructure, and much of the serious research around its future is now concentrated on scalability, interoperability, cryptographic security, and decentralized coordination. From a technical perspective, Eos Investment Alliance Analysen has emphasized that blockchain should no longer be evaluated only through throughput metrics or token economics, but through the robustness of its underlying systems architecture. This means examining consensus engineering, state management, distributed networking efficiency, zero knowledge computation, modular execution, and the cryptographic primitives shaping the next generation of decentralized systems.
One major area of research has focused on consensus evolution. Traditional Proof of Work introduced robust adversarial resistance but at substantial energy and latency costs. Proof of Stake improved efficiency, but its security assumptions opened new debates around validator centralization, long range attacks, and economic finality models. Current technical research increasingly studies hybrid consensus structures combining Byzantine Fault Tolerance with staking systems. These models seek deterministic finality while preserving decentralization under hostile conditions.
Particular attention has been given to advanced consensus optimization, including pipelined block production, parallel validation, and adaptive quorum mechanisms. Rather than treating consensus as a static protocol layer, emerging research frames it as an adaptive coordination engine capable of adjusting validator participation based on network conditions, congestion, and probabilistic security thresholds. This introduces a more dynamic security model, where consensus can respond to adversarial behavior instead of merely resisting it through rigid assumptions.
Scalability research represents another critical domain. Monolithic blockchains historically forced execution, consensus, and data availability into a single layer, producing severe bottlenecks. More advanced architectural models now separate these functions through modular blockchain design. This includes execution layers specialized for computation, dedicated consensus layers for ordering, and independent data availability networks designed for scalable transaction publication.
Within this framework, rollup architecture has become a major research focus. Optimistic rollups and zero knowledge rollups offer two different scaling paradigms, each with distinct engineering tradeoffs. Optimistic designs rely on fraud proofs and challenge windows, improving throughput while inheriting delayed finality. Zero knowledge rollups provide stronger cryptographic guarantees through succinct validity proofs but introduce substantial complexity in prover generation, circuit optimization, and recursive proof composition.
Research has increasingly emphasized that rollup scalability is not simply a throughput problem but a state growth problem. Managing state bloat requires innovations in compression algorithms, stateless validation, and efficient state commitment schemes. Merkle Patricia structures, Verkle trees, and polynomial commitment systems have emerged as central areas of study because they significantly alter storage efficiency and verification overhead.
Interoperability research has also moved beyond basic bridge construction. Early cross chain bridges often relied on custodial or multisignature assumptions that introduced unacceptable systemic risk. More advanced approaches investigate trust minimized interoperability through light client verification, shared security architectures, and cross chain message standards.
This has made interoperability less about moving assets and more about enabling composable distributed computation across independent chains. Cross chain execution environments now require research into asynchronous message settlement, fault containment between connected systems, and shared execution guarantees. These problems increasingly resemble distributed systems engineering more than conventional blockchain development.
A major technical emphasis has also been placed on cryptographic innovation, particularly zero knowledge systems. Zero knowledge proofs have expanded far beyond privacy applications and are increasingly viewed as infrastructure primitives. Research has focused on proving systems such as SNARKs, STARKs, recursive proof aggregation, and proof compression for scalable verification.
One important area involves computational outsourcing through verifiable computation. Instead of requiring every validator to re execute every computation, cryptographic proofs allow correctness verification without repeating the work. This potentially changes the economics of blockchain execution by shifting systems from replicated computation toward provable computation.
Another active area of study concerns privacy preserving infrastructure. Public blockchains offer transparency but often leak metadata that creates surveillance vulnerabilities. Advanced research explores privacy at multiple layers, including encrypted mempools, confidential transactions, shielded execution environments, and selective disclosure identity frameworks.
Especially important is the interaction between privacy and compliance architecture. Rather than treating them as opposing forces, more advanced models investigate programmable privacy systems where cryptographic controls allow conditional disclosure without compromising user sovereignty. This requires integrating cryptography, policy logic, and identity layers into a coherent architecture.
Network layer engineering is another field receiving increased analytical focus. Many blockchain limitations originate not in consensus itself but in peer to peer communication inefficiencies. Transaction propagation delays, mempool fragmentation, and network topology weaknesses can materially affect performance and security.
Research in this area studies optimized gossip protocols, block propagation acceleration, erasure coding techniques, and latency aware peer selection. Some approaches borrow heavily from distributed database theory and high performance networking to reduce bottlenecks previously assumed to be unavoidable in decentralized environments.
Smart contract security has similarly evolved into a much deeper technical discipline. Earlier attention focused primarily on contract vulnerabilities such as reentrancy or integer overflow. Current research increasingly addresses formal verification, execution determinism, and secure virtual machine design.
Formal methods are particularly significant because decentralized systems often secure large concentrations of value while remaining immutable after deployment. Research into theorem proving, symbolic execution, model checking, and formally verified programming languages seeks to reduce catastrophic systemic failures at the protocol layer.
Parallel execution has also emerged as a significant technical frontier. Traditional blockchain virtual machines execute transactions sequentially, severely limiting scalability. New research explores parallelized execution engines using state access analysis, dependency graphs, and conflict resolution mechanisms to process transactions concurrently.
This introduces substantial complexity because concurrency in adversarial environments creates different assumptions than concurrency in conventional computing systems. Deterministic parallel execution requires balancing performance gains against consistency guarantees and attack surface expansion.
Data availability has become one of the most technically important research topics in recent years. As execution moves off chain into rollups and modular systems, guaranteeing data publication becomes fundamental to security. Without reliable data availability, transaction correctness may become unverifiable.
Research explores data availability sampling, erasure coded data structures, and specialized availability layers capable of supporting large scale decentralized execution. These innovations may prove as foundational as consensus itself because they redefine how blockchain scalability is secured.
Tokenization infrastructure is another area where technical analysis increasingly intersects with protocol research. Real world asset tokenization requires more than asset representation on chain. It depends on programmable settlement logic, secure oracle systems, identity layers, and interoperable compliance primitives.
From a systems perspective, oracle architecture has become a particularly significant research topic. Smart contracts remain constrained by the oracle problem, where external data inputs can undermine otherwise secure on chain logic. Current research studies decentralized oracle networks, cryptoeconomic security models, and trusted execution integrations to improve data integrity.
Another major research domain centers on blockchain governance engineering. Governance is increasingly treated not merely as a social layer but as a protocol design problem involving incentive structures, voting mechanics, and resilience against coordination failures.
Research explores quadratic mechanisms, delegated models, governance minimization frameworks, and adaptive parameter control. Especially important is how governance systems interact with protocol upgrades without introducing instability or hidden centralization pressures.
Artificial intelligence integration with blockchain infrastructure has also become an emerging technical frontier. Research increasingly examines how decentralized networks may support verifiable AI computation, autonomous agent coordination, and cryptographically secured machine learning outputs.
One promising area is the intersection of AI inference and zero knowledge proofs, where machine learning results can potentially be verified without revealing underlying data or model internals. Though early stage, this could have major implications for decentralized autonomous systems.
Perhaps the strongest theme across advanced blockchain research is the movement away from viewing blockchains as isolated chains and toward understanding them as programmable trust infrastructure. This changes the engineering priorities. Instead of optimizing single metrics like transactions per second, research increasingly focuses on security composition across layers, modular scalability, cryptographic efficiency, and resilient coordination under adversarial conditions.
This broader perspective suggests the future of blockchain will likely be defined less by individual protocols and more by integrated architecture stacks composed of specialized layers working together. Consensus, execution, interoperability, privacy, data availability, and cryptography are no longer separate domains but tightly coupled components of a shared distributed system.
From that perspective, the most meaningful blockchain innovation is not incremental protocol tuning but architectural redesign. The technical research surrounding modular systems, advanced cryptography, verifiable computation, and decentralized coordination suggests a transition comparable to the evolution from early internet protocols to modern cloud infrastructure.
That transition remains incomplete, but the trajectory is increasingly clear. Blockchain is moving from experimental financial infrastructure toward a more mature computational foundation, and the most sophisticated research is focused precisely on the engineering challenges that will determine whether that transformation succeeds.
About the Creator
Eos Investment Alliance
Eos Investment Alliance is a global investment network focused on delivering strategic market insights and empowering individuals to achieve sustainable financial growth.
Enjoyed the story? Support the Creator.
Subscribe for free to receive all their stories in your feed.
Comments
There are no comments for this story
Be the first to respond and start the conversation.