
Your Employees Are Already Using AI. Your Data Is Already at Risk.
The case for private, internal AI co-pilots, and why enterprises can't afford to wait another quarter.
There is a policy in place at most enterprises right now. It says employees should not paste sensitive data into public AI tools. Nobody follows it.
A 2024 report found that workers submitted confidential business data into ChatGPT and similar tools in 6.5% of all interactions — a number that has likely grown since. Source code. Customer lists. Internal financial projections. HR records. All of it typed into a chat window connected to a third-party model, trained on the internet, governed by terms of service most IT teams have never read fully.
This is the real security crisis of 2026. It is not a dramatic breach. It is a slow, daily leak happening through the front door.
Shadow AI Is Now a Boardroom Problem
Shadow IT used to mean an unauthorized Dropbox account. Today, it means employees running business decisions through public LLMs without flagging it to anyone.
The pattern is predictable. A sales manager pastes a deal brief into Claude or GPT to get a summary. A developer drops proprietary code into Copilot to fix a bug faster. A finance analyst feeds a spreadsheet into an AI tool to generate a report. None of these people is acting maliciously. They are just doing their jobs faster.
The problem is that public AI models are not designed for corporate confidentiality. Data submitted through these platforms may be used for training, stored on third-party servers, or exposed through model inversion attacks. Most enterprise legal teams would be alarmed if they reviewed the average employee's prompt history from the past six months.
The hidden cost here is not just compliance. It is competitive exposure. When your proprietary processes, client data, and internal strategy feed into a public model, you lose control of your most valuable information assets.
Why Off-the-Shelf Wrappers Are Not Enough
The first wave of enterprise AI products tried to solve this with wrapper tools — essentially a branded interface sitting on top of GPT-4 or another public model, with some access controls bolted on.
These tools helped with usability. They did not solve the underlying data problem. The model itself still lives outside your firewall. Your data still leaves your environment. You are still subject to a third party's data retention policies.
The better approach — and the one gaining traction among serious IT leaders — is to build a private, internal AI co-pilot that runs on your infrastructure, trained only on your approved data, and accessible only to your team.
This is what the shift to custom AI development looks like in practice.
How Private AI Co-Pilots Actually Work
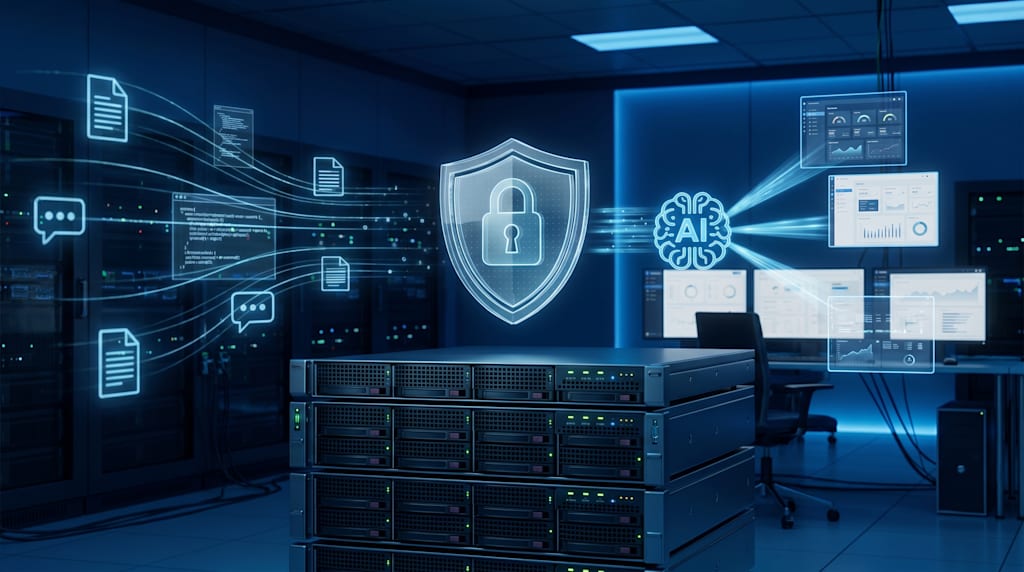
The technical foundation behind these systems is called Retrieval-Augmented Generation (RAG). Instead of relying on a general-purpose model's training data, RAG connects a language model to your own internal knowledge bases — documentation, databases, past communications, product specs — at the point of answering a query.
Here is what that means practically. When an employee asks the internal AI a question, the model retrieves only the relevant documents from your secure internal library and generates an answer from those. No internet access. No third-party data sharing. No public model training pipeline touches your proprietary content.
The model itself can be deployed on a private cloud instance, an on-premise server, or a secured environment — depending on your compliance requirements. HIPAA, SOC 2, GDPR — the architecture can be built to respect these frameworks from the ground up, not retrofitted afterward.
Companies like ViitorCloud are building exactly this type of system for enterprises and growing mid-market companies. The approach involves isolating data pipelines, building custom retrieval layers, and connecting AI assistants directly to internal tools like ERP systems, CRMs, and project management platforms — all within a controlled environment.
This Is Not Optional for Your 2026 Roadmap
Digital transformation has always been about giving people better tools. The risk in 2026 is that you give your employees no official AI tools, and they build their own workarounds using whatever is available. That is the scenario IT leaders need to prevent.
The organizations moving fastest right now are not the ones that banned AI. They are the ones who replaced the risky behavior with a safer, better alternative. A private co-pilot that actually knows the company's internal documentation is more useful to an employee than a general-purpose chatbot. It gives better answers, reduces errors, and removes the temptation to paste sensitive data somewhere it should not go.
Building that system requires working with an AI consulting and strategy partner who understands both the model architecture and the security requirements. This is specialized work. A general-purpose software vendor will struggle with the RAG pipeline design. A pure AI research shop may not understand enterprise compliance frameworks.
The decision is straightforward. Your employees want AI assistance. The question is whether that assistance happens inside a secure, controlled system your IT team manages — or outside it, one risky prompt at a time.
The cost of waiting is already visible in your prompt logs. Most IT teams have not looked yet.
About the Creator
ViitorCloud Technologies
As a leading software development company, we’ve empowered 500+ startups, SMBs, and enterprises to transform their operations. Upgrade your business with our AI-First Software and Platforms that automate and scale, keeping you future-ready.
Enjoyed the story? Support the Creator.
Subscribe for free to receive all their stories in your feed.
Comments
There are no comments for this story
Be the first to respond and start the conversation.