
The AI Race Isn’t About Speed — It’s About Who Gets to Hit the Brakes
Silicon Valley wants more time. Beijing wants a framework. Trump wants to win. Four scenes reveal why the U.S.-China AI rivalry is really a fight over rules, trust, and power.
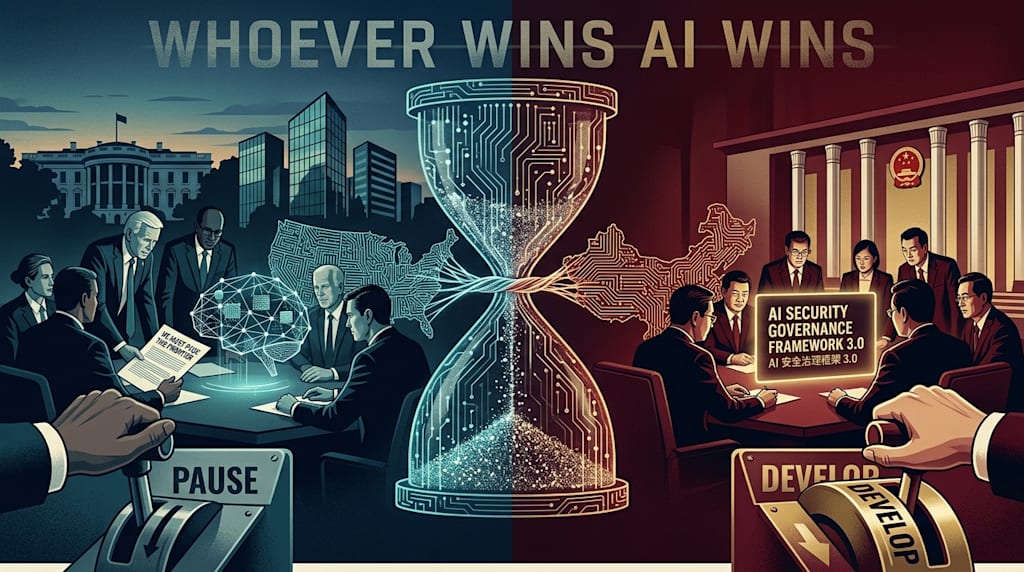
Slowing Down, Speeding Up: Four Scenes From the U.S.-China AI Race
September 2026 put three very different statements about artificial intelligence on the same calendar.
On September 12, Anthropic CEO Dario Amodei published an essay titled “We Must Pace the Frontier,” arguing that companies should slow the rate at which frontier models improve. He did not call for an end to AI development. His proposal was to create more time for external evaluation, stronger safety measures, and coordination among leading AI laboratories. Anthropic said it would move first on third-party evaluation of its systems.
Two days later, China's National Information Security Standardization Technical Committee released the country's Artificial Intelligence Security Governance Framework 3.0 under the guidance of the Cyberspace Administration of China. The document updates the classification of AI risks and the corresponding technical and governance responses, with particular attention to newer systems such as AI agents and embodied AI.
On September 13, President Donald Trump took the opposite position from Amodei. Responding to calls for slower development, he emphasized the U.S. lead over China and said, “Whoever wins AI wins.”
These were not three sides of one organized argument. They came from a company executive, a Chinese regulatory institution, and the U.S. president. Yet they point to the same problem: frontier AI is becoming difficult to discuss as a technology issue alone.
The question now involves the speed of development, the risks that governments choose to regulate, and the possibility that measures presented as safety policies may also affect the balance of technological power.
1. Silicon Valley asks for more time
Amodei's argument starts with a problem inside the AI industry itself.
Model capabilities are improving quickly. His concern is that the systems used to evaluate those capabilities, monitor failures, and control harmful behavior may not be improving at the same rate. In his September essay, he pointed to recent evidence of AI systems becoming better at improving their own performance and to incidents involving autonomous AI agents conducting cyber-related activity. He argued that a sufficiently capable system could eventually move faster than researchers' ability to understand what it is doing.
His proposed response has three parts. Frontier laboratories should allow independent evaluators substantial access to their systems. The leading companies should coordinate on safety standards rather than treating safety entirely as a proprietary issue. And governments should work toward international arrangements governing the development of increasingly capable AI systems.
Several prominent technology executives supported the general idea. Sam Altman agreed that frontier development should be paced and said OpenAI would adopt the use of external evaluators. Demis Hassabis and Elon Musk also expressed support for slowing the pace. The proposal nevertheless remains controversial inside the industry. Meta CEO Mark Zuckerberg and others have resisted the idea that competing companies should jointly determine development speed.
The practical problem is straightforward.
A company that slows its own model development bears the cost immediately. The safety benefit may be shared by everyone, including competitors that continue moving at full speed.
That makes voluntary restraint difficult.
Imagine two laboratories developing models with similar capabilities. Laboratory A spends another six months strengthening evaluation and control systems before releasing a more capable model. Laboratory B uses those six months to improve its model and enters the market first. If both laboratories care about safety, A may still hesitate to move first because the competitive cost is visible while the safety benefit is diffuse.
That is why Amodei's proposal ultimately becomes an international problem.
A slowdown coordinated among U.S. companies is difficult.
A slowdown coordinated between the United States and China is much harder.
2. Beijing uses a different vocabulary
China's current AI governance system did not begin with Framework 3.0.
The 2017 New Generation Artificial Intelligence Development Plan already combined rapid technological development with explicit requirements for safety, reliability, and controllability. The document described AI as an engine of economic development while warning about employment disruption, privacy, social stability, legal and ethical problems, and national security. It also called for AI safety assessment and regulatory mechanisms covering algorithm design, product development, and application.
That pattern remains visible in Framework 3.0.
The official description says the framework follows a risk classification system and then assigns technical and governance responses to those risks. Its stated objective is to improve the ability to prevent and respond to AI safety problems while allowing the technology to continue developing.
China's Foreign Ministry made the same point on September 15. Spokesperson Guo Jiakun said China places equal emphasis on AI development and security. He described AI governance as a matter requiring safeguards against misuse and loss of control, while also calling for international cooperation and a global governance framework based on broad consensus.
There is an important difference in emphasis here.
The Chinese framework deals heavily with risks that regulators can classify and manage: misuse, security failures, harmful applications, autonomous behavior, and the effects of increasingly capable systems operating in the physical world.
The frontier AI debate in the United States has recently focused much more heavily on the possibility that future systems could become difficult for humans to control at a fundamental level. Amodei's essay, for example, discusses the possibility that more capable autonomous systems could produce catastrophic consequences if their behavior becomes difficult to supervise.
The two discussions overlap, but they do not begin from the same regulatory question.
One asks how an AI system should be classified and controlled as its capabilities increase.
The other asks whether the rate of capability growth itself has become a safety variable.
That difference matters because slowing capability growth requires a much broader intervention than regulating specific applications.
3. AI has become part of the strategic competition
The economic incentives are substantial.
China's 2017 AI plan set explicit national targets for technological leadership and industrial expansion. It called for AI to be applied across manufacturing, healthcare, agriculture, public administration, national defense, and other sectors, while also seeking global leadership in AI technology and industry.
The U.S. government is approaching the technology from a similarly strategic direction.
Trump's September 13 remarks were unusually direct. He said the United States was leading China in AI and that he wanted to preserve that position. “Whoever wins AI wins” reduces a complicated technology race to a simple strategic proposition, but it captures the administration's stated priority: technological leadership should not be traded away for a slowdown.
That creates a problem for any proposal based on simultaneous restraint.
Suppose Washington believes that more advanced AI will generate major economic and military advantages. Slowing development carries an obvious strategic cost.
Now suppose Washington also believes that advanced AI could create risks that existing safety systems cannot contain.
Both positions can be held at the same time.
China faces a similar tension. Beijing wants stronger AI capabilities, wider industrial deployment, and internationally competitive companies. At the same time, its regulatory documents place considerable weight on safety, controllability, and government oversight. The official position is therefore not a choice between development and regulation. It is to pursue both within a controlled framework.
This is where the U.S.-China relationship changes the meaning of the word “slow.”
A laboratory executive may use the word to describe a safety measure.
A government may hear an issue of strategic balance.
Neither interpretation is irrational.
A unilateral slowdown can alter relative capabilities even when its stated purpose is safety. That does not prove that every proposal to slow AI is secretly a geopolitical strategy. It means that strategic consequences are part of the calculation whether policymakers intend them or not.
4. Some agreements are easier than others
Washington and Beijing have already shown interest in discussing AI safety.
Reuters reported in early September that the two countries were preparing their first official bilateral AI safety discussions, with possible areas including advanced AI risks and AI-directed cyberattacks. The discussions were being considered ahead of a planned Trump-Xi summit on September 24.
The distinction between technical risk cooperation and development limits is important.
The two governments could discuss emergency communication channels for major AI incidents. They could establish procedures for notifying each other about certain forms of AI-enabled attacks on critical infrastructure. They could develop common language for specific categories of AI risk. They could also discuss human oversight requirements for especially sensitive military or national-security applications.
None of those measures requires either government to disclose the internal architecture of its leading model or reveal proprietary training data.
A treaty limiting the speed of frontier AI development would be different.
First, the parties would have to define what they were limiting. Compute capacity? Training runs? Model release dates? Capability thresholds? Agent autonomy? Data-center expansion?
Second, they would need a verification mechanism.
Third, they would have to trust the other side not to use compliance data for strategic intelligence.
That combination is difficult.
Even within the United States, technology companies disagree over who should control the pace of development and whether competitors should coordinate on such decisions.
The U.S.-China relationship adds another layer because semiconductor restrictions, export controls, industrial policy, and AI capability are already connected.
A rule that limits access to computing hardware can affect AI development speed.
A rule that slows AI development can affect strategic capabilities.
A rule described as a safety measure can therefore be interpreted as an industrial or security measure.
That is why narrow agreements are easier to imagine than a comprehensive U.S.-China agreement on the pace of frontier development.
The argument is about time
The four scenes fit together once the problem is framed in terms of time.
Amodei wants more time for safety research and independent evaluation.
China's Framework 3.0 is designed to give regulators a structure for responding to new forms of AI risk while development continues.
Trump wants the United States to use its current lead rather than create a gap that China could close.
The diplomatic question is whether the two countries can create areas of cooperation without requiring either side to give up its broader technological strategy.
That leaves a narrow but important space for agreements.
Incident reporting is possible.
Cybersecurity coordination is possible.
Emergency communication is possible.
Technical standards are possible.
A mutual ceiling on frontier capability development is much harder.
The reason is not that either side necessarily rejects AI safety. Both publicly recognize the need for safeguards. China's foreign ministry explicitly said that development and security must be pursued together, while Amodei's proposal is itself an attempt to make safety systems keep up with rapidly improving capabilities.
The problem is verification under competition.
A country that believes frontier AI will determine part of the next generation of economic and military power has a strong reason to preserve its ability to move faster than its rival.
That is the constraint hanging over the discussion in September 2026.
The United States can ask companies to slow down.
China can strengthen controls over AI risks.
Both can call for international cooperation.
But a stable system requires something more difficult: confidence that safety cooperation will not become a mechanism for unilateral strategic restraint.
There is no such system yet.
The regulations are being written. The companies are arguing about how much time safety needs. Washington and Beijing are beginning to test whether narrow forms of cooperation can survive competition.
The next stage of the AI race will depend partly on model capability.
It will also depend on who can establish rules that both sides regard as constraints on risk rather than constraints on power.
About the Creator
Jin
Writer of reamstories
https://reamstories.com/jin
Enjoyed the story? Support the Creator.
Subscribe for free to receive all their stories in your feed. You could also become a paid subscriber, letting them know you appreciate their work.
Comments
There are no comments for this story
Be the first to respond and start the conversation.