
HIPAA Just Raised the Floor on Healthcare Security. Here's What Pen Tests Must Cover Now.
Annual testing is moving from "best practice" to a written rule. The systems that need attention have grown faster than most security teams realized.
The HIPAA Security Rule has not seen a major rewrite since 2013. That run is ending.
In December 2024, the U.S. Department of Health and Human Services issued a Notice of Proposed Rulemaking. The proposed update reshapes how covered entities and business associates handle electronic protected health information. The proposal introduces mandatory encryption of ePHI at rest and in transit, required multi-factor authentication, 72-hour incident reporting, annual penetration testing, and enhanced business associate oversight. Medcurity
Industry coverage notes that the proposed rule mandates vulnerability scanning at a minimum every six months and annual penetration testing for all systems handling ePHI under 45 CFR § 164.308(a)(1)(ii)(B).
You can review the official proposed rule directly through the HHS Office for Civil Rights HIPAA Security Rule update page.
The proposed rule remains in the finalization process as of mid-2026. Healthcare organizations preparing now will face fewer surprises than those waiting for the final text. This article walks through what the scope actually looks like.
Why the Rules Tightened
The numbers tell the story.
Between 2009 and 2025, 7,418 healthcare data breaches affecting 500 or more individuals were reported to OCR. Those breaches exposed the protected health information of more than one billion Americans — 1,013,066,481 to be precise, which is more than 2.9 times the current U.S. population.
The Change Healthcare attack alone affected 192.7 million people in 2024.
IBM's 2025 Cost of a Data Breach Report shows U.S. data breaches set a new record at $10.22 million, increasing 9.2% from $9.36 million in 2024. Healthcare remains the costliest sector for the fourteenth consecutive year.
Those numbers explain why regulators stopped treating penetration testing as an optional control. Voluntary best practice produced too many breaches.
What Annual Pen Tests Must Cover
Healthcare pen testing in 2026 has a wider surface area than most teams expect. The required scope includes systems that most security audits used to skip.
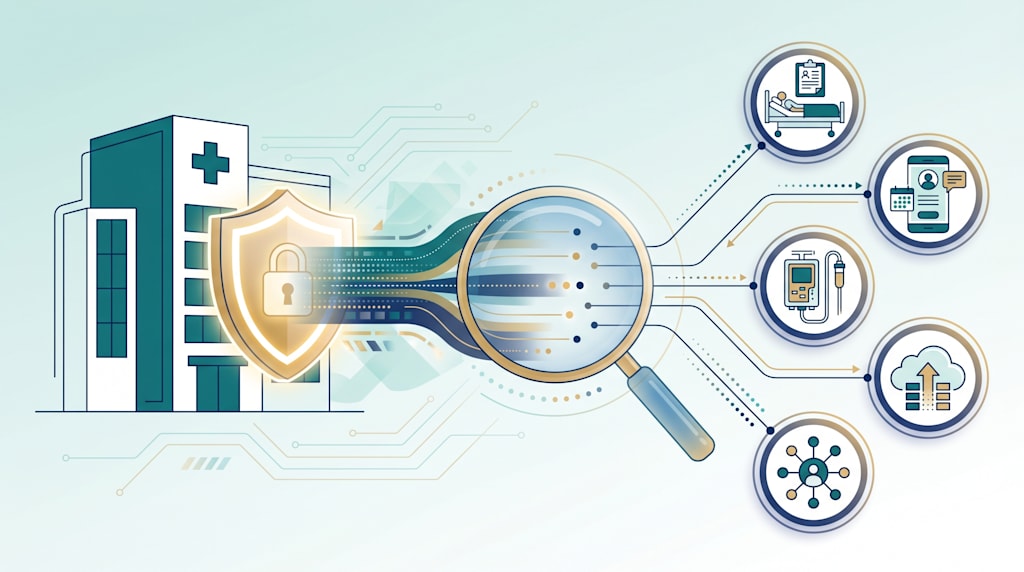
EHR and core clinical applications: Electronic health record systems sit at the center of every healthcare environment. Pen testers check authentication paths, role-based access controls, audit logging, and APIs that connect EHRs to other systems. A weak EHR integration often becomes the path used by attackers.
Patient portals and telehealth platforms: These public-facing applications expose ePHI to the open internet. Pen testers look at session management, password reset flows, two-factor enrollment, and any feature that lets patients upload or download records. Telehealth platforms add video and chat surfaces that need separate attention.
Medical device security: Connected infusion pumps, imaging devices, and monitoring equipment now sit on hospital networks. Many run outdated firmware. Some lack any update path. A pen test scopes these devices for unauthenticated access, default credentials, and lateral movement risk.
Business associate connections: The proposed rule expands business associate oversight. Pen testers review the boundary between covered entity systems and vendor environments. VPN tunnels, API integrations, and shared file systems all qualify as test targets.
Cloud infrastructure: Healthcare workloads run across AWS, Azure, and Google Cloud. Pen tests check identity and access management configurations, storage bucket permissions, network segmentation, and any misconfigured service exposing ePHI.
Internal networks: Healthcare networks remain flat in many organizations. A pen tester who gets inside the perimeter through a phishing simulation tests how far the access can spread. Network segmentation gaps surface here.
How Pen Testing Differs From Vulnerability Assessment
Both controls show up in the proposed rule. They serve different jobs.
A vulnerability assessment scans systems for known weaknesses. Outdated software. Missing patches. Misconfigurations. Automated tools handle most of the work. The output is a list of findings sorted by severity.
A penetration test sends a trained specialist to attempt actual exploitation. The tester chains weaknesses together. They mimic real attacker behavior. The output documents what an attacker could actually accomplish, not just what tools could theoretically exploit.
Both controls work together. The vulnerability scan tells you what exists. The pen test tells you whether defenses hold under pressure.
What a HIPAA Pen Test Report Should Include
The report becomes part of the HIPAA security audit documentation. OCR examiners will ask for it. The structure matters.
A complete report includes the scope definition, the methodology used, the timeline of testing activity, and the qualifications of the testing team. The findings section documents each issue with severity ratings, evidence of exploitation, and remediation recommendations.
The executive summary translates technical findings into business risk. A board reviewing the report should understand what the findings mean for patient safety, regulatory exposure, and operational continuity.
Documentation gaps create their own compliance risk. A pen test that lacks proper documentation may satisfy the testing requirement on paper. It will not survive an OCR investigation following a breach.
Where Healthcare Organizations Hit Walls
Three problems show up across pen test engagements.
The first is scope confusion. Teams sometimes test only their newest applications. Legacy systems get skipped because they feel too fragile. Attackers target legacy systems specifically. The scope must include them.
The second is medical device security. Hospital biomedical teams own the devices. IT security owns the network. Neither team always owns the testing budget. The result is a coverage gap that attackers find quickly.
The third is the gap between testing and remediation. A pen test that finds 50 issues but produces no fix timeline does not improve security posture. The follow-up work matters more than the test itself.
The Practical Path Forward
Most healthcare organizations work with specialized pen testing firms for the actual security work. The internal team manages scope, remediation, and audit documentation.
Development partners play a different role. Custom patient portals, EHR integrations, and patient-facing applications need to be built with the new requirements in mind. Companies like ViitorCloud, which writes about how penetration testing services support HIPAA compliance, focus on the development practices that make systems easier to pass through security testing. The cleaner the code, the fewer findings the pen test produces.
Healthcare pen testing has shifted into a documented control under federal law. The systems that need coverage extend across EHRs, portals, medical devices, cloud workloads, and business associate connections. The cost of skipping any of these has climbed past $10 million per incident.
The organizations preparing now will treat the annual pen test as part of their operating rhythm. The organizations that delay will spend the next two years catching up. The rule did not change because regulators wanted more paperwork. It changed because the patient data losses kept getting bigger.
About the Creator
ViitorCloud Technologies
As a leading software development company, we’ve empowered 500+ startups, SMBs, and enterprises to transform their operations. Upgrade your business with our AI-First Software and Platforms that automate and scale, keeping you future-ready.
Enjoyed the story? Support the Creator.
Subscribe for free to receive all their stories in your feed.
Comments
There are no comments for this story
Be the first to respond and start the conversation.