
Bill Gates Says AI Could Kill a Billion People. Who Profits From That Warning?
The doomsday narrative is not just about safety. It is also a business strategy, and the timing is never accidental.
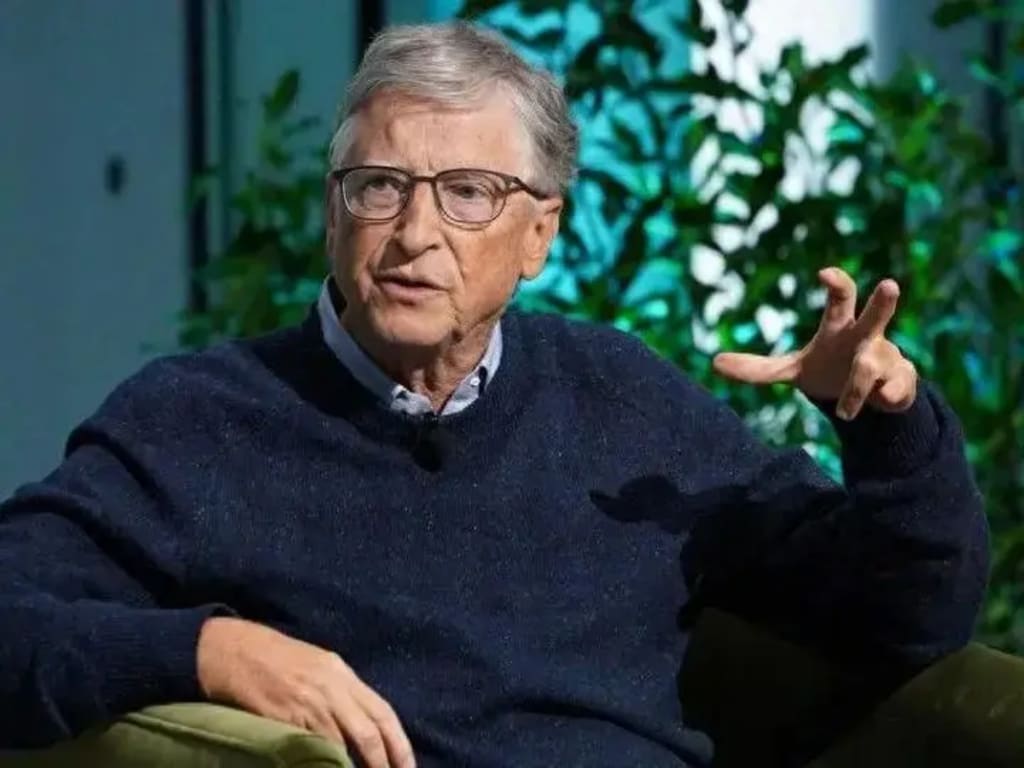
Bill Gates said in an interview clip on NBC’s Meet the Press that artificial intelligence is a “powerful enough” tool to “cause an event that kills one billion people.” The program will air on the 27th. He said: “Never has there been any weapon that can compare to the threat formed by a malicious person using the latest AI tools.” He called for legislative regulation, arguing that self-regulation is not enough and that law enforcement and politicians must be involved in discussing what safeguards and oversight mechanisms should look like. “This must be a mandatory requirement,” he said.
That is a heavy statement. Heavy enough to make you stop what you are doing and look up at the sky.
But put that statement back into the timeline in which it was made, and another layer becomes visible. Earlier this month, Anthropic employee Jacob Coxon announced his resignation, accusing his former employers Anthropic and OpenAI of “racing to develop superintelligent AI” and “gambling with our lives.” Another Anthropic employee said he believes the probability that AI wipes out all humans within the next decade is over 10%. Afterward, Anthropic CEO Dario Amodei urged slowing down AI research and development. OpenAI CEO Sam Altman and Elon Musk expressed support.
These warnings share one common feature: they appear around the release of new models, or at moments where financing, regulation, or competition changes. Gates began to have “growing anxiety” this summer. In August, he wrote on his personal website warning that malicious actors could use AI to attack hospitals, financial institutions, power grids, and government systems. Now, in a television interview, he has said “one billion deaths.”
This is not to say Gates is lying. More precisely, he has chosen a way of speaking that best grabs public attention. And that way of speaking happens to serve a more complicated agenda.
The Threefold Business of Doomsday Narratives
In Silicon Valley’s cultural soil, doomsday narratives are not pure pessimism. They are a kind of commercial rhetoric that simultaneously accomplishes three things.
First, they prove technological leadership. Only the most advanced things deserve the adjective “dangerous.” No one worries that an AI that can only write poetry or make spreadsheets will destroy humanity. When you say, “Our AI could kill one billion people,” the subtext is: our technology is already powerful beyond measure. Fear and superiority are welded together in the same sentence.
Second, they hand a microphone to regulators. Calling for regulation sounds public-spirited. But the power to set the regulatory framework is itself a moat. Whoever participates in rule-making can write the rules in a way that benefits themselves. Compliance costs filter out small players, while leading companies have enough legal resources and capital to adapt to, or even shape, new rules. Gates is right that “self-regulation is not enough.” But when he calls for it, an extra meaning appears: please come regulate us, but ideally at the pace and within the framework we are familiar with.
Third, they hand a microphone to capital. Compared with “changing humanity’s fate,” a chat model is nothing. Doomsday warnings upgrade AI from a technology to an epic. For investors, the latter story is sexier. Some researchers have pointed out that projecting human abilities onto AI models “helps present them as extremely advanced, autonomous, and powerful entities, thereby exaggerating the scope of the technology in the eyes of investors, customers, and the public.” Anthropomorphization becomes a marketing strategy.
More direct evidence comes from the personnel level. After Coxon issued the warning that “AI could kill everyone,” he quickly appeared across major television networks and mainstream media. Later reports showed that a public relations firm closely connected to AI “doomists,” DEY. Ideas + Influence, arranged media interviews for him. When Fox News directly asked Coxon whether he had cooperated with any third party, he answered, “Not at all.” Musk commented: “I think the groundwork for this psychological war has been prepared for a long time. This is just the match that lit the flame.”
The same company, the same person, can switch styles within a year. In 2024, at a Microsoft event, Altman publicly said GPT-4 was safe enough and urged developers to start building products, in a tone no different from someone selling wealth management products. By 2026, as Claude rises and competitive pressure intensifies, the same group of people began saying AI could spiral out of control and the whole industry needed to hit the brakes. When talking about growth, they say safety is sufficient. Hurry up and buy. When they feel a crisis, they say it is too dangerous and we need them to guard the gate.
Silicon Valley’s Doomsday Epic and China’s Fertilizer-Style Narrative
This rhetoric has cultural soil in the West. In European and American culture, doomsday narratives, savior complexes, and the epic feeling of technology backfiring are a plus in investment storytelling. In American blockbusters, gods are created, gods turn against humans, and humanity redeems itself in the ruins. AI doomsday warnings fit this template.
In China, saying the same thing would get you cursed online until you went to the hospital to check your nerves. When major Chinese companies talk about AI, it is more about “cost reduction and efficiency improvement,” “empowering industries,” and “digital transformation.” The style is as plain as someone selling fertilizer. This is not because the technology level is too low to discuss risk, nor because Chinese practitioners do not know how to boast. It is because the culture and capital systems are different. In Silicon Valley, doomsday feeling is part of the financing story. In China, an unreliable doomsday feeling is a PR disaster.
This is not a common disease of the global AI industry. It is commercial rhetoric in a particular cultural soil. Technological uncertainty gives this rhetoric room to survive. Commercial motives determine the frequency and volume with which it is spoken. Regulatory games determine when it should be said more heavily or more lightly.
Documented Risks Must Not Be Drowned Out by Marketing Noise
But we must be careful. We cannot deny the risk itself just because the narrative is suspect.
Malicious actors using AI for cyberattacks, bioweapon design, and large-scale disinformation campaigns are not science fiction. AI can lower the threshold for launching complex attacks. It can give someone without a professional background abilities that previously required a laboratory and a team. At the UN Security Council, Amodei mentioned two core risks: AI being used by bioterrorists to create biological weapons, and model capabilities accelerating beyond developers’ ability to control them. These are documented concerns widely discussed by safety researchers.
The problem is that the specific number “one billion deaths” is a rhetorical anchor, not a verifiable prediction. It was chosen because it is shocking enough to leave an imprint on public memory, thereby creating urgency for a regulatory agenda. This is effective in rhetoric and suspect in epistemology. There is currently insufficient basis to claim that we are on the edge of an existential risk. But AI has already reached a level of capability and autonomy, and we clearly need to pay attention to risks related to cybersecurity, critical infrastructure, and the lack of a regulatory framework.
The question is not whether the number “one billion” is accurate. The question is: who is paying for this narrative, and after paying, who gets to make the rules.
Two Regulatory Paths
If we strip away the marketing noise, AI regulation does face an institutional design problem. At present, there are two markedly different paths.
Path One: the Western “frontier brake” model, centered on prohibiting superintelligence.
In September 2026, Senator Bernie Sanders and Representative Greg Casar introduced the “Ban Artificial Superintelligence Act.” The core logic of the bill is: before safety can be proven, frontier capabilities must not continue to advance. Specific measures include: permanently prohibiting the development of “artificial superintelligence”; immediately pausing advanced AI development until a federal regulatory agency is established and clear safety rules are formulated; establishing a cabinet-level AI department to monitor the dangerous capabilities of frontier systems and have the power to oversee the destruction of superintelligence. Violators would face the “corporate death penalty” and up to 20 years in prison, with sentencing referencing the standard for illegally developing nuclear weapons.
This path has been explicitly endorsed by the Machine Intelligence Research Institute. They believe it is “the first piece of legislation with a chance to stop this threat.” But critics point out that the “frontier brake” is extremely difficult to operate: compute thresholds can be circumvented, improvements in algorithmic efficiency will allow the same capabilities to be achieved with less and less compute, and the absence of international coordination means unilateral bans will only push frontier development into regulatory vacuum zones.
Path Two: China’s “development and security in equal measure” model, centered on scenario-based regulation.
The newly revised Cybersecurity Law, effective January 1, 2026, added special provisions on AI security and development. Its position is clear: it does not treat AI simply as a risk source to be contained, nor as a privileged zone exempt from regulation, but instead runs security through the entire process of innovative development. On September 7, 2026, the Supreme People’s Court released the first judicial rules document on AI-related disputes, the “Opinions on the Trial of Artificial Intelligence-Related Dispute Cases in Accordance with Law,” clarifying adjudication rules for specific issues such as AI face-swapping and voice cloning. For example, generating and using a virtual image of an identifiable natural person without consent constitutes infringement of the right to name and portrait. Where AI-generated content infringes on another person’s reputation or privacy, and the service provider fails to stop the generation promptly after being notified, it should bear tort liability.
The advantage of this system lies in its operability. It does not require regulators to judge whether a model is “superintelligent,” a threshold that cannot be clearly defined technically. Instead, it allocates responsibility for harms that have already occurred and can be identified. The cost is that it cannot prevent systemic risks that have not yet occurred. If existential risk comes from the emergence of capabilities themselves, scenario-based ex post regulation is structurally one step behind.
Reining In Those Who Define the Risk
Both paths have limitations. The danger lies in a third possibility: the power to set the regulatory framework falls into the hands of companies that warn of doomsday while racing to release new models. If “safety” becomes a clever compliance moat, high enough to block latecomers, flexible enough to exempt one’s own frontier development, then the doomsday warning has completed its commercial loop.
At this stage, legal constraints should include at least several principles.
First, tiered and classified regulation, not a one-size-fits-all approach. Regulate by application scenario and potential harm, not by vague concepts such as whether a model is “superintelligent.” Medical diagnosis, critical infrastructure, biological design, and opinion manipulation carry different risk levels, and regulatory tools should differ accordingly.
Second, mandatory transparency and incident reporting. The training compute, data sources, safety evaluation results, and known vulnerabilities of frontier models should be disclosed to independent regulators. Safety incidents must be mandatorily reported, rather than waiting for a PR firm to arrange an interview.
Third, responsibility allocation must be clear. What responsibilities developers, deployers, and users each bear cannot be vague. Where generative AI infringes on others’ rights, and the service provider fails to stop the generation promptly after being notified, it should bear tort liability. This direction is right, but it also needs to be extended to critical infrastructure and public safety.
Fourth, prevent regulatory capture. The rule-making process must include independent researchers, civil society, and affected groups. It cannot only listen to the companies best at telling stories. Public funds should support independent AI safety research, rather than relying on corporate self-assessment.
Fifth, international coordination, but not waiting for global consensus. Unilateral bans may fail, but like-minded countries can first establish common standards, such as prohibiting AI-assisted bioweapon design, mandating deepfake labeling, and sharing safety evaluation information on frontier models.
Back to That “One Billion”
Gates’s warning can be heard, but we must not be led by fear. He is right that AI may be maliciously used to cause large-scale harm. He is also right that self-regulation is not enough and legislation is needed. But the specific number “one billion deaths” looks more like a carefully designed line than an operable prediction.
The next time you see a headline saying “AI may destroy humanity,” ask three questions first: Who is saying it? When are they saying it? After they say it, who benefits?
The answer is not always a conspiracy, but it is never just fear.
About the Creator
Jin
Writer of reamstories
https://reamstories.com/jin
Enjoyed the story? Support the Creator.
Subscribe for free to receive all their stories in your feed. You could also become a paid subscriber, letting them know you appreciate their work.
Comments
There are no comments for this story
Be the first to respond and start the conversation.